Embedded systems fundamentals for reliable smart hardware design
Embedded systems fundamentals in one view
Embedded systems fundamentals are the hardware, firmware, timing, memory, interface, power, safety, and security principles that make a dedicated computing system behave predictably inside a physical product. Unlike a general-purpose computer, an embedded system is usually built for a specific job: reading sensors, making control decisions, driving actuators, communicating with other devices, and staying within defined limits for cost, energy use, size, temperature, and response time.
For smart hardware teams, these fundamentals matter because product failures rarely come from one isolated component. A missed interrupt can affect a motor. A weak power rail can corrupt memory. A poorly designed update process can turn a connected device into a field-support problem. Embedded design is therefore best treated as a complete system discipline: the product must sense, compute, act, communicate, and recover under real operating conditions.
What makes an embedded system different
An embedded system is a computer built into a larger product, machine, or infrastructure asset. It may be visible to the user, as in a smart thermostat, or almost invisible, as in a battery management unit, industrial controller, medical sensor, vehicle subsystem, or appliance control board. Its defining feature is not size alone. The defining feature is that computing is tied to a real-world function.
Public engineering references use similar framing. Arm education material describes embedded learning around processors, peripherals, interrupts, and the concurrent operation of hardware and software. NIST Special Publication 1900-202, published in 2019, describes cyber-physical and IoT systems as systems that combine embedded sensors, processors, and actuators to interact with the physical world. Both descriptions point to the same practical lesson: embedded design is about controlled interaction between digital logic and physical behavior.
That interaction creates constraints that web, desktop, or cloud software rarely face in the same form. The system may need to respond within microseconds or milliseconds. It may run for years on a battery. It may have kilobytes or megabytes of RAM rather than gigabytes. It may also need to keep operating safely when a sensor fails, a packet is lost, or a user removes power at the wrong moment.
- Dedicated function: the device is designed around a product task rather than general computing.
- Real-world inputs and outputs: sensors, actuators, displays, radios, switches, motors, relays, and analog signals are central to the design.
- Resource limits: memory, processing headroom, energy, board space, and bill of materials cost shape design decisions.
- Timing requirements: some functions must complete before a real-world deadline, not merely as soon as possible.
- Long lifecycle expectations: industrial and appliance products may need maintainable firmware for many years.
The core architecture stack
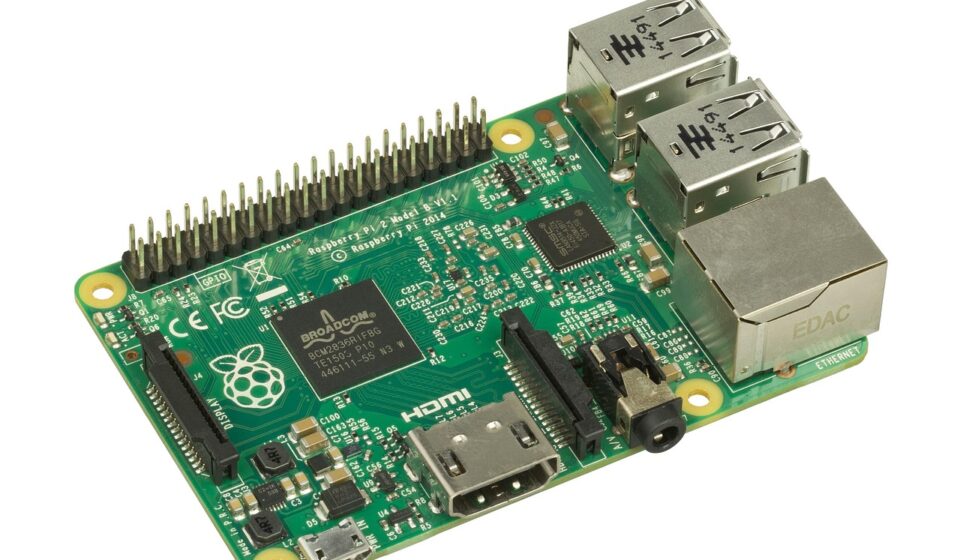
A practical embedded architecture can be viewed as a stack, even when the final product is physically small. At the bottom are the power supply, clock sources, reset circuitry, sensors, actuators, and board-level interfaces. Above that is the processing device, often a microcontroller, microprocessor, digital signal processor, FPGA, or system-on-chip. Above the silicon are startup code, device drivers, middleware, application logic, diagnostics, and update mechanisms.
The processor choice is one of the earliest architectural decisions. A microcontroller usually combines CPU, flash, RAM, timers, analog functions, and communication peripherals in a single chip. It is common in battery devices, control loops, and cost-sensitive products. A microprocessor is more suitable when the product needs high-level operating systems, advanced user interfaces, large memory, cameras, databases, or heavy networking. Many smart hardware products use both: a microprocessor for high-level applications and a microcontroller for deterministic control.
Memory is another fundamental design constraint. Flash stores program code and constants. RAM stores stack, heap, buffers, real-time data, and task state. Non-volatile memory may store calibration data, device identity, counters, logs, and configuration. A common early-stage mistake is to treat memory as an implementation detail. In embedded systems, memory layout affects boot time, reliability, update safety, fault recovery, and the maximum complexity the product can support.
Interfaces turn computing into product behavior. GPIO reads buttons and controls simple signals. ADCs convert analog sensor values. PWM drives motors, LEDs, heaters, and power electronics. I2C and SPI connect local sensors and memory devices. UART, CAN, LIN, Ethernet, USB, Bluetooth, Wi-Fi, and cellular links support communication beyond the board. Each interface brings tradeoffs in speed, wiring, noise tolerance, complexity, and software overhead.
Firmware, timing, and real-time behavior
Firmware is the software that makes embedded hardware useful. At a minimum, it initializes clocks and memory, configures peripherals, reads inputs, runs decision logic, controls outputs, and handles errors. In simple products, this may be a bare-metal loop with interrupt handlers. In more complex products, the firmware may use a real-time operating system, or RTOS, to schedule multiple tasks with defined priorities.
The key timing question is whether the system must be fast, deterministic, or both. A fast system performs many operations per second. A deterministic system performs required operations within known timing bounds. Motor control, power conversion, sampling, communication stacks, safety interlocks, and sensor fusion often depend more on predictable latency than on peak benchmark performance.
Interrupts are central to real-time behavior. An interrupt lets hardware signal that something needs immediate attention, such as a timer event, received byte, ADC completion, or fault pin change. Good interrupt design keeps handlers short, avoids unnecessary blocking, and moves noncritical work into scheduled tasks or main-loop processing. Poor interrupt design can create latency spikes, missed events, race conditions, and difficult debugging.
An RTOS adds task scheduling, queues, semaphores, timers, and synchronization tools. FreeRTOS documentation describes the kernel as a real-time operating system used across many architectures and suited to embedded microcontroller applications. The design benefit is not automatic reliability; the benefit is structure. Developers still need to choose task priorities carefully, manage shared resources, avoid deadlocks, and measure worst-case behavior.
| Firmware layer | Main responsibility | Common risk if ignored |
|---|---|---|
| Startup and boot | Initialize clocks, memory, vector tables, and safe default states | Unstable power-up behavior or unsafe outputs during reset |
| Drivers | Control peripherals such as timers, ADCs, UARTs, SPI, I2C, and GPIO | Hardware features are used incorrectly or inconsistently |
| Middleware | Provide protocol stacks, file systems, RTOS services, and device libraries | Hidden memory, timing, or licensing problems appear late |
| Application logic | Implement product behavior, control rules, modes, and user interaction | Feature code becomes tightly coupled to hardware details |
| Diagnostics and recovery | Detect faults, log events, reset safely, and support service workflows | Field failures are hard to reproduce or repair |
Power, memory, and reliability tradeoffs
Embedded design is often a tradeoff exercise. A faster processor may shorten active time but increase peak current. A larger buffer may prevent data loss but reduce available RAM for tasks and stacks. A more sophisticated wireless protocol may improve features while increasing certification, antenna, and power-management complexity. Fundamentals help teams make these tradeoffs deliberately instead of discovering them during late-stage testing.
Power design is especially important for smart hardware. Low-power firmware is not only about putting the CPU to sleep. It also means controlling sensors, radios, regulators, clocks, pull-up resistors, memory devices, and wake sources as a coordinated system. Battery-powered devices need energy budgets based on real duty cycles, not only datasheet standby numbers. Mains-powered products still need robust power sequencing, surge tolerance, thermal planning, and safe behavior during brownouts.
Memory reliability also deserves attention. Stack overflow, heap fragmentation, buffer overflow, uninitialized data, and flash wear can all create intermittent failures. Many teams avoid dynamic memory allocation in small real-time systems after startup, or use it only under strict rules. Static analysis, code review, memory maps, stack watermarking, and fault injection can reveal problems before production.
Reliability is broader than avoiding firmware bugs. It includes environmental margins, electromagnetic compatibility, connector durability, clock accuracy, watchdog strategy, manufacturing variation, and serviceability. A watchdog timer, for example, is not a substitute for fixing a lockup. It is a recovery mechanism that should be paired with fault logging and a safe restart path. See also: BUYING GUIDES.
Safety and security are design fundamentals
Safety and security should not be treated as late add-ons. In embedded systems, a software defect or cyber weakness can affect physical behavior. NIST guidance for operational technology emphasizes that security controls in physical systems must account for performance, reliability, and safety requirements. That is a different environment from conventional IT systems, where delaying a transaction may be acceptable but delaying a control response may not be.
Functional safety focuses on reducing unacceptable risk when a system can cause harm. IEC 61508 is widely used as a foundational standard for electrical, electronic, and programmable electronic safety-related systems, and sector-specific standards build on similar lifecycle thinking. Not every smart device requires formal safety certification, but the engineering discipline is still valuable: identify hazards, define safe states, analyze failure modes, verify assumptions, and document evidence.
Security fundamentals include secure boot, signed firmware updates, protected debug access, unique device identity, encrypted communication where appropriate, least-privilege software design, and a plan for vulnerability response. The update mechanism is particularly important for connected devices. A device that cannot be updated safely may carry known defects for its entire field life; a device with a weak update process can be damaged or compromised at scale.
Coding guidelines also matter. MISRA C and related industry practices exist because C remains common in embedded firmware and because undefined or implementation-dependent behavior can undermine safety, portability, and analysis. These guidelines are not magic checklists, but they encourage predictable language use, reviewable structure, and tool-supported verification.
A practical development workflow
A strong embedded workflow starts before schematic capture and coding. The team should define what the product must do, what it must never do, how quickly it must respond, what conditions it must survive, how it will be updated, and how failures will be diagnosed. These requirements should be specific enough to test. “Low power” is vague; average current below a defined threshold during a defined duty cycle is testable.
Architecture follows requirements. Engineers choose processing, memory, power, sensing, actuation, communication, and enclosure strategies together. Early prototypes should validate the riskiest assumptions: sensor noise, motor load, radio range, thermal rise, boot time, latency, current consumption, and manufacturability. For more articles on connected devices and controller design, browse our embedded systems coverage.
Bring-up is the stage where hardware and firmware first meet. Teams verify rails, clocks, reset behavior, programming access, GPIO states, communication buses, boot logs, and peripheral operation. A disciplined bring-up checklist prevents random debugging and reduces the chance of damaging boards. Oscilloscopes, logic analyzers, current probes, debuggers, and trace tools are not optional luxuries in serious embedded work; they are how engineers see timing and electrical behavior that code alone cannot explain.
Testing should combine unit tests, hardware-in-the-loop tests, integration tests, environmental checks, long-run stress tests, update and rollback tests, and fault injection. The goal is not only to prove the happy path. The goal is to understand how the system behaves when inputs are noisy, communication is interrupted, memory is near its limit, power is unstable, or a peripheral returns unexpected data.
- Define measurable requirements for function, timing, power, safety, security, cost, and environment.
- Create a hardware and firmware architecture that assigns responsibility clearly.
- Prototype the riskiest sensors, actuators, power modes, and communication paths first.
- Bring up boards with a repeatable checklist and record deviations.
- Measure timing, current, memory use, and thermal behavior under realistic workloads.
- Test failure modes, recovery paths, firmware updates, and manufacturing procedures.
Frequently asked questions
Are embedded systems fundamentals mostly hardware or software?
They are both. A useful embedded engineer does not need to be an expert in every component, but must understand how firmware decisions affect hardware behavior and how hardware limits affect firmware design. Timing, power, memory, and interfaces sit between the two disciplines.
Is an RTOS required for every embedded product?
No. Many reliable products use bare-metal firmware when the control flow is simple and timing is manageable. An RTOS becomes useful when the system has multiple concurrent activities, communication stacks, periodic control tasks, or maintainability needs that are difficult to handle cleanly in one loop.
What is the difference between a microcontroller and an embedded system?
A microcontroller is a chip that includes processing, memory, and peripherals. An embedded system is the complete product function built around processing, firmware, electronics, interfaces, mechanical constraints, power, and real-world behavior. A microcontroller is often part of an embedded system, not the whole system.
Which fundamentals should beginners learn first?
Start with C or C++ basics, digital I/O, timers, interrupts, serial communication, ADCs, PWM, memory layout, debugging, and reading datasheets. Then add RTOS concepts, low-power design, secure updates, test strategy, and safety analysis as projects become more complex.
Why do embedded bugs feel harder to reproduce?
Many embedded bugs depend on timing, electrical conditions, memory state, temperature, power sequencing, or external devices. A bug may appear only when several conditions align. That is why measurement tools, logs, controlled tests, and clear fault-handling design are essential parts of embedded engineering.
The bottom line
Embedded systems fundamentals are not a checklist of isolated topics. They are the shared engineering language that connects processors, firmware, sensors, actuators, power, timing, safety, security, and testing. Smart hardware becomes reliable when these decisions are made together and verified with real measurements. For teams building connected, battery-powered, industrial, or safety-relevant devices, mastering the fundamentals is the most practical way to reduce late redesigns and improve field performance.